A Third Way Between Private and Public AI

Australian AI cloud provider Sharon AI plans to host frontier AI models onshore, next to customers' sensitive data. It will use a new confidential computing capability from VAST Data.

VAST DataEnclave is built on NVIDIA Confidential Computing. It is designed to let banks, hospitals and government agencies run proprietary models on sensitive data without it leaving local infrastructure. Model owners do not have to expose their intellectual property either.

DataEnclave is being previewed now and will ship in Q1 2027 through VAST Data and OEM partners including Cisco and Supermicro.

Until now, organisations wanting AI on sensitive data have broadly faced two choices. They could run open or custom models on their own infrastructure, or send data to a cloud provider to use its models.

Many regulated organisations cannot move data to an external AI service. At the same time, model builders have been unwilling to distribute proprietary model weights into infrastructure they do not control.

DataEnclave aims to resolve that impasse. Each party encrypts its own assets with its own keys. The enterprise controls the keys to its data, and the model builder controls the keys to its model weights.

Before anything is decrypted, the hardware environment is cryptographically verified, a process known as attestation. Only then are the data and model loaded into a secure enclave, where they remain protected in CPU and GPU memory during processing.

Infrastructure operators and administrators cannot see either the data or the model while processing takes place, according to VAST.

Sovereignty that can be demonstrated

"Our customers across Australia and Asia-Pacific need to run AI at full speed without compromising on data sovereignty, and increasingly they also want access to frontier models that were previously only available offshore," said James Manning, CEO and Co-founder, Sharon AI.

"DataEnclave lets us host those models onshore, inside attested environments where the model owner's weights and the customer's data are both protected from everyone, including us. That gives our customers the flexibility to operate on their own terms, backed by sovereignty they can demonstrate, not just declare."

VAST says model builders including Cohere, CrowdStrike, Deepgram, Factory, Fundamental, NVIDIA and TwelveLabs are supporting the platform. Their models can run inside customer data centres or trusted cloud hardware.

NVIDIA Confidential Computing encrypts guest memory, GPU memory and NVLink traffic. This isolates active data and models from operators, administrators and other tenants sharing the same hardware.

Bring Your Own Key Management System integrations allow enterprises and model builders to hold their keys in their own trust domains. VAST says this also protects an enterprise's own fine-tuned model weights.

Deployments can be connected or fully air-gapped. Attestation services are built on the open CNCF Trustee stack, or delivered in partnership with Fortanix.

Attestation events, key releases and enclave lifecycle actions are recorded in a tamper-proof, queryable audit trail in the VAST DataBase. VAST says this shows what ran, where and under what verified policy, without exposing protected data or weights.

The same secure runtime provides isolated sandboxes for AI agents through VAST AgentEngine, enforcing policy over the data, tools and actions agents can access.
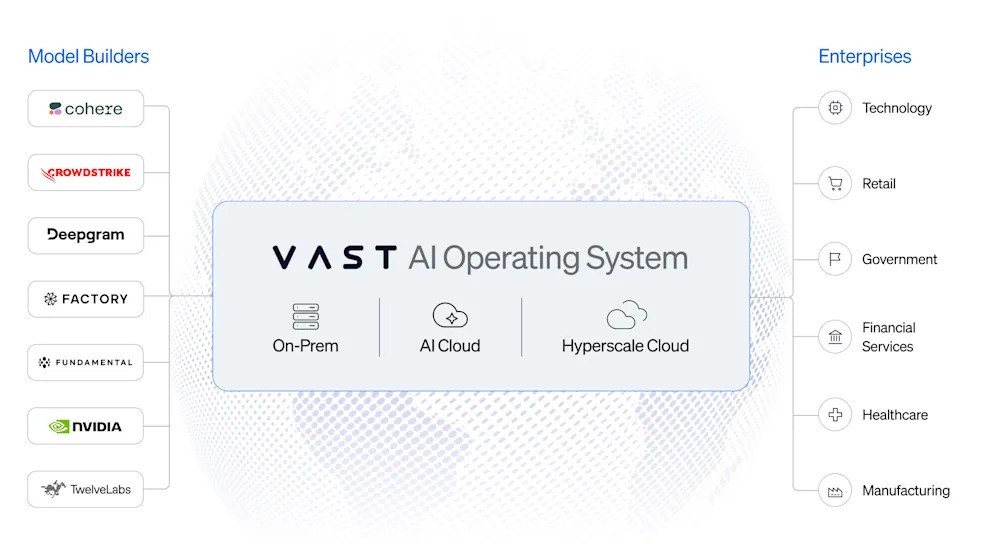
VAST AI schematic

Models as managed resources

VAST positions the launch as part of a broader shift in which its AI Operating System manages models alongside data. That includes deciding where models run, what data they can access and who can use them.

"Models are becoming a resource the operating system has to manage, the same way it manages data," said Renen Hallak, Founder and CEO, VAST Data.

"Customers around the world have unique regulatory and sovereignty requirements, and they are asking for AI that is encrypted end-to-end - not just at rest but in motion and during inference," said Frank O'Dowd, Chief Revenue and Commercial Officer, Cohere.

Because isolation is enforced in hardware, VAST says sovereign and regional AI clouds can establish verifiable trust without dedicating entire machines to a single tenant.

Australian AI cloud provider Sharon AI plans to host frontier AI models onshore, next to customers' sensitive data. It will use a new confidential computing capability from VAST Data.

VAST DataEnclave is built on NVIDIA Confidential Computing. It is designed to let banks, hospitals and government agencies run proprietary models on sensitive data without it leaving local infrastructure. Model owners do not have to expose their intellectual property either.

DataEnclave is being previewed now and will ship in Q1 2027 through VAST Data and OEM partners including Cisco and Supermicro.

Until now, organisations wanting AI on sensitive data have broadly faced two choices. They could run open or custom models on their own infrastructure, or send data to a cloud provider to use its models.

Many regulated organisations cannot move data to an external AI service. At the same time, model builders have been unwilling to distribute proprietary model weights into infrastructure they do not control.

DataEnclave aims to resolve that impasse. Each party encrypts its own assets with its own keys. The enterprise controls the keys to its data, and the model builder controls the keys to its model weights.

Before anything is decrypted, the hardware environment is cryptographically verified, a process known as attestation. Only then are the data and model loaded into a secure enclave, where they remain protected in CPU and GPU memory during processing.

Infrastructure operators and administrators cannot see either the data or the model while processing takes place, according to VAST.

Sovereignty that can be demonstrated

"Our customers across Australia and Asia-Pacific need to run AI at full speed without compromising on data sovereignty, and increasingly they also want access to frontier models that were previously only available offshore," said James Manning, CEO and Co-founder, Sharon AI.

"DataEnclave lets us host those models onshore, inside attested environments where the model owner's weights and the customer's data are both protected from everyone, including us. That gives our customers the flexibility to operate on their own terms, backed by sovereignty they can demonstrate, not just declare."

VAST says model builders including Cohere, CrowdStrike, Deepgram, Factory, Fundamental, NVIDIA and TwelveLabs are supporting the platform. Their models can run inside customer data centres or trusted cloud hardware.

NVIDIA Confidential Computing encrypts guest memory, GPU memory and NVLink traffic. This isolates active data and models from operators, administrators and other tenants sharing the same hardware.

Bring Your Own Key Management System integrations allow enterprises and model builders to hold their keys in their own trust domains. VAST says this also protects an enterprise's own fine-tuned model weights.

Deployments can be connected or fully air-gapped. Attestation services are built on the open CNCF Trustee stack, or delivered in partnership with Fortanix.

Attestation events, key releases and enclave lifecycle actions are recorded in a tamper-proof, queryable audit trail in the VAST DataBase. VAST says this shows what ran, where and under what verified policy, without exposing protected data or weights.

The same secure runtime provides isolated sandboxes for AI agents through VAST AgentEngine, enforcing policy over the data, tools and actions agents can access.

VAST AI schematic

Models as managed resources

VAST positions the launch as part of a broader shift in which its AI Operating System manages models alongside data. That includes deciding where models run, what data they can access and who can use them.

"Models are becoming a resource the operating system has to manage, the same way it manages data," said Renen Hallak, Founder and CEO, VAST Data.

"Customers around the world have unique regulatory and sovereignty requirements, and they are asking for AI that is encrypted end-to-end - not just at rest but in motion and during inference," said Frank O'Dowd, Chief Revenue and Commercial Officer, Cohere.

Because isolation is enforced in hardware, VAST says sovereign and regional AI clouds can establish verifiable trust without dedicating entire machines to a single tenant.