Details have been published of a critical flaw in the programming language PHP, which is the backbone of more than 70% of all websites. Left unfixed, the flaw would allow hackers to easily take over and compromise millions of websites and the information held on their servers. In response, multiple European governments and operators including the Port of Rotterdam have taken websites offline.
Updating WordPress, Drupal or a plugin will not close the PHP flaws that took government websites offline this week. The vulnerable code sits in the PHP engine underneath them, so every server, appliance and hosting platform running PHP has to be found and updated.
Attackers have used a stolen credential from a Microsoft 365 backup service to sign in to hundreds of customer tenants. Because backup tools need broad access to mail, files and directories, the attackers inherited that access.
Data concerns have delayed or derailed AI projects at 86 per cent of organisations in the past 12 months. That is despite 95 per cent naming better use of data to improve business outcomes as a top priority.
A quarter of enterprise security breaches will trace back to AI agent abuse by 2028, Gartner predicts. It blames unmanaged machine privileges and legacy credential practices.
Australian organisations will no longer be able to summarise their cyber security posture with a single Essential Eight maturity level. The Australian Signals Directorate (ASD) has released a principles-based replacement that rates security area by area.
Origin Energy has seen no evidence that customer data taken in its July cyber incident has been published online, but chairman Scott Perkins has told shareholders the risk remains and affected customers must stay alert to scams.
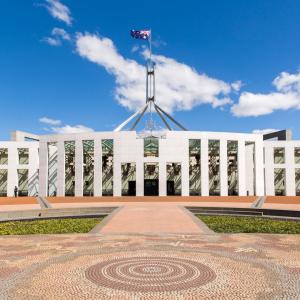
The department that operates the Australian Parliament House's computing network has implemented seven of the mandatory Essential Eight cyber security strategies below the required standard, the Australian National Audit Office has found.
Organisations running on-premises SharePoint should patch immediately and hunt for signs of compromise, after the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed active exploitation of three vulnerabilities affecting every supported version of the platform.
Russian state-sponsored actors are exploiting poorly configured and unpatched network devices across critical infrastructure worldwide, using weaknesses as basic as default SNMP community strings, a 20-agency international advisory warns.
Patient records including consultation notes, referral letters and pathology results have been stolen from general practices across five Australian states and territories, in a cyber attack on health services provider Partnered Health.
Microsoft 365 Copilot has switched from Anthropic’ s Claude to OpenAI's new GPT-5.6, the company's latest flagship model family, as the preferred AI model across Word, Excel, PowerPoint, Copilot Chat and Cowork. The change comes two months after Microsoft made Anthropic's Claude the default model in several of the same applications, and marks the latest shift in an ongoing contest between the two AI labs for position inside Microsoft's productivity platform.
From 1 July 2026, Australia’s expanded Anti-Money Laundering and Counter-Terrorism Financing regime will extend to a broader range of professions, including lawyers, accountants, real estate agents and other designated non-financial businesses and professions.
Almost half the ICT hardware devices operating across 10 South Australian government agencies qualify as legacy systems, the state's Auditor-General has found. Incomplete asset inventories and inconsistent risk reporting are leaving agencies with reduced visibility of the security risks these systems create.
Data breach notifications hit record highs on both sides of the Tasman in 2025, with regulators in Australia and New Zealand both pointing to cyber attacks and vendor security gaps as the common thread.
Boards need to treat the deployment of agentic AI as a delegation decision rather than a technology purchase, according to a new white paper from the Governance Institute of Australia. Unlike generative AI, which produces outputs for human review, agentic AI systems act on those outputs directly, transacting with customers and executing multi-step workflows with limited human oversight.
Eighty-seven per cent of Australian Government agencies now use artificial intelligence, but only 15 per cent apply it to information management activities and just 8 per cent use it to create metadata, according to the National Archives of Australia's latest Check-up survey.